From the research team.

Analyses of live campaigns, notes on how the platform works, and where we have been.

  1. SCENE 1: SoupDealer - Technical Analysis of a Stealth Java Loader Used in Phishing Campaigns Targeting Türkiye SoupDealer, a three-stage Java loader spread by phishing in Türkiye, slipped past public sandboxes, AV and EDR. How it works, and what Threat.Zone caught.
  2. Technical Analysis of Phishing Campaigns Targeting the Defense Industry Delivering Snake Keylogger A phishing campaign impersonating TUSAŞ sends Turkish defense and aerospace firms a Snake Keylogger variant disguised as a contract. Our technical analysis.
  3. Introducing the Syscalls Feature in Threat.Zone: Unveiling Granular Malware Analysis Introducing Syscalls: Gain deep insights into malware with Threat.Zone's new feature for advanced threat analysis!
  4. Unveiling Perspectives: Advanced Malware Masterclass Workshops in Istanbul & Ankara We hosted 2 Advanced Malware Masterclass Workshops in Istanbul & Ankara. Here is how they went.
  5. Origins of A Logger - Agent Tesla Recent research by Berk Albayrak and Utku Corbaci, the team members of Malwation Threat Research (MTR) team has focused on BEC attacks targeting the company's employees. You can find the white paper from their findings in this post.
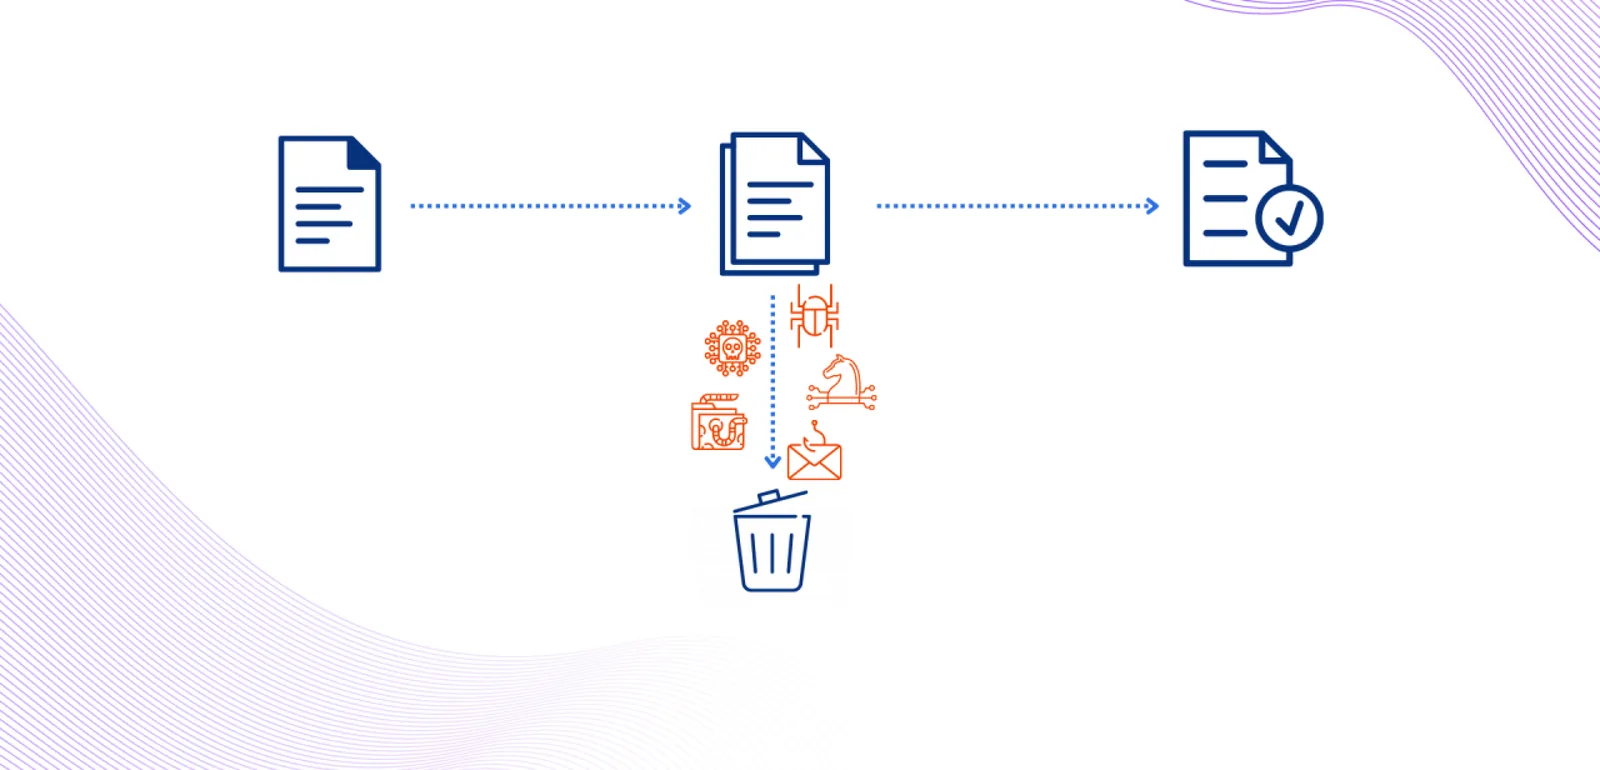
  6. Content Disarm and Reconstruction (CDR): Nice-to-Have or Must Have? What is the Cost of No Action? What is CDR? Is it a nice-to-have or a must have? What are the risks of no actions? We gathered them all in this blog post!
  7. Highlights from the 9th e-Safe Cybersecurity Summit Here are the highlights of the 9th e-Safe Cybersecurity Summit from where we returned with an award for year's cybersecurity product, Threat.Zone-in Malware Detection/Analysis.
  8. From Crime Scene to Cyber Scene: How the CSI Module Speeds Up Malware Forensics Speed up malware forensics with Threat.Zone's CSI module: rapid access to artifacts, tools, and secure analysis.
  9. Introducing Our New URL Scan Feature in Threat.Zone Proud to present Threat.Zone’s new feature: URL Scan. You can fetch and analyze files from URLs, plus URL Reputation & Threat Analysis with Threat.Zone's URL Analysis feature.
  10. Reflections of Virus Bulletin 2024 from our Head of Revops’ POV: A Unique Experience in Security I had a great experience at Virus Bulletin 2024, here is my recap of the event including key insights, networking, and our team's talk.
  11. Static Malware Analysis vs Dynamic Malware Analysis - Comparison Chart Learn about the main differences between static and dynamic malware analysis with their pros and cons to understand why both are essential.
  12. Malwation is a Proud Member of AMTSO We are thrilled to announce that Malwation is now a proud member of the Anti-Malware Testing Standards Organization (AMTSO)!
  13. Meet Malwation in Dublin - Gold Sponsor for Virus Bulletin 2024 Meet Malwation at Virus Bulletin 2024 in Dublin and explore our malware analysis innovations.
  14. The Importance of Multi-OS Sandbox Solutions in Today's Cybersecurity As organizations expand, so does their attack surface. Protect your entire infrastructure with multi-OS sandboxing.
  15. Overview of Malware Landscape in First Half of 2024 Learn the Malware Landscape in the first Half of 2024 from this blog post with malware types and malware families and their real-time samples.
  16. Simplest Yet Most Common and Effective Evasion Tactic: Sleep! In this blog post, you will learn how "Sleep" function is used to evade detection with real-life examples and how to overcome it!
  17. Advanced Malware Traffic Analysis We explained how Threat.Zone’s Advanced Malware Traffic Analysis enhances malware detection with real-life samples and insights. Check it out now!
  18. New MuddyWater Campaigns After Operation Swords of Iron MuddyWater APT targets critical sectors with spear-phishing attacks using RMM tools. Stay vigilant against BEC threats with the information in this blog post.
  19. ACH Analysis of Lockbit Attacks in Turkey Analyzing claims of LockBit ransomware targeting Turkey post-OpCronos. False flags or real attacks? Let's see!
  20. Malwation 3rd Investment Announcement Malwation is proud to announce the successful completion of its third investment round, a significant milestone that underscores the...
  21. Cortex XSOAR & MALWATION AIMA Integration Accelerate malware analysis, detection and response processes by integrating Cortex XSOAR with AIMA.
  22. Testing Antivirus with Malwation MSP MSP stands for Malware Simulation Platform and it’s designed to create sophisticated and customizable malwares on cloud for testing and comparing antiviruses...
  23. Offensive Approach to Online Sandboxes In this blog, we will share our research about manipulating online sandboxes and how to automatize this process with MSP.
  24. Overcome the Detection Challenges of EDR and Antivirus Tools with Malwation CDR In today’s rapidly evolving digital landscape, the battle between cybercriminals and cybersecurity professionals continues to intensify.